Spencer Brawner
I'm a Toronto-based security practitioner writing about AI security, privacy, and the controls organizations need when agents can act on their behalf.
More than 20 years building security programs
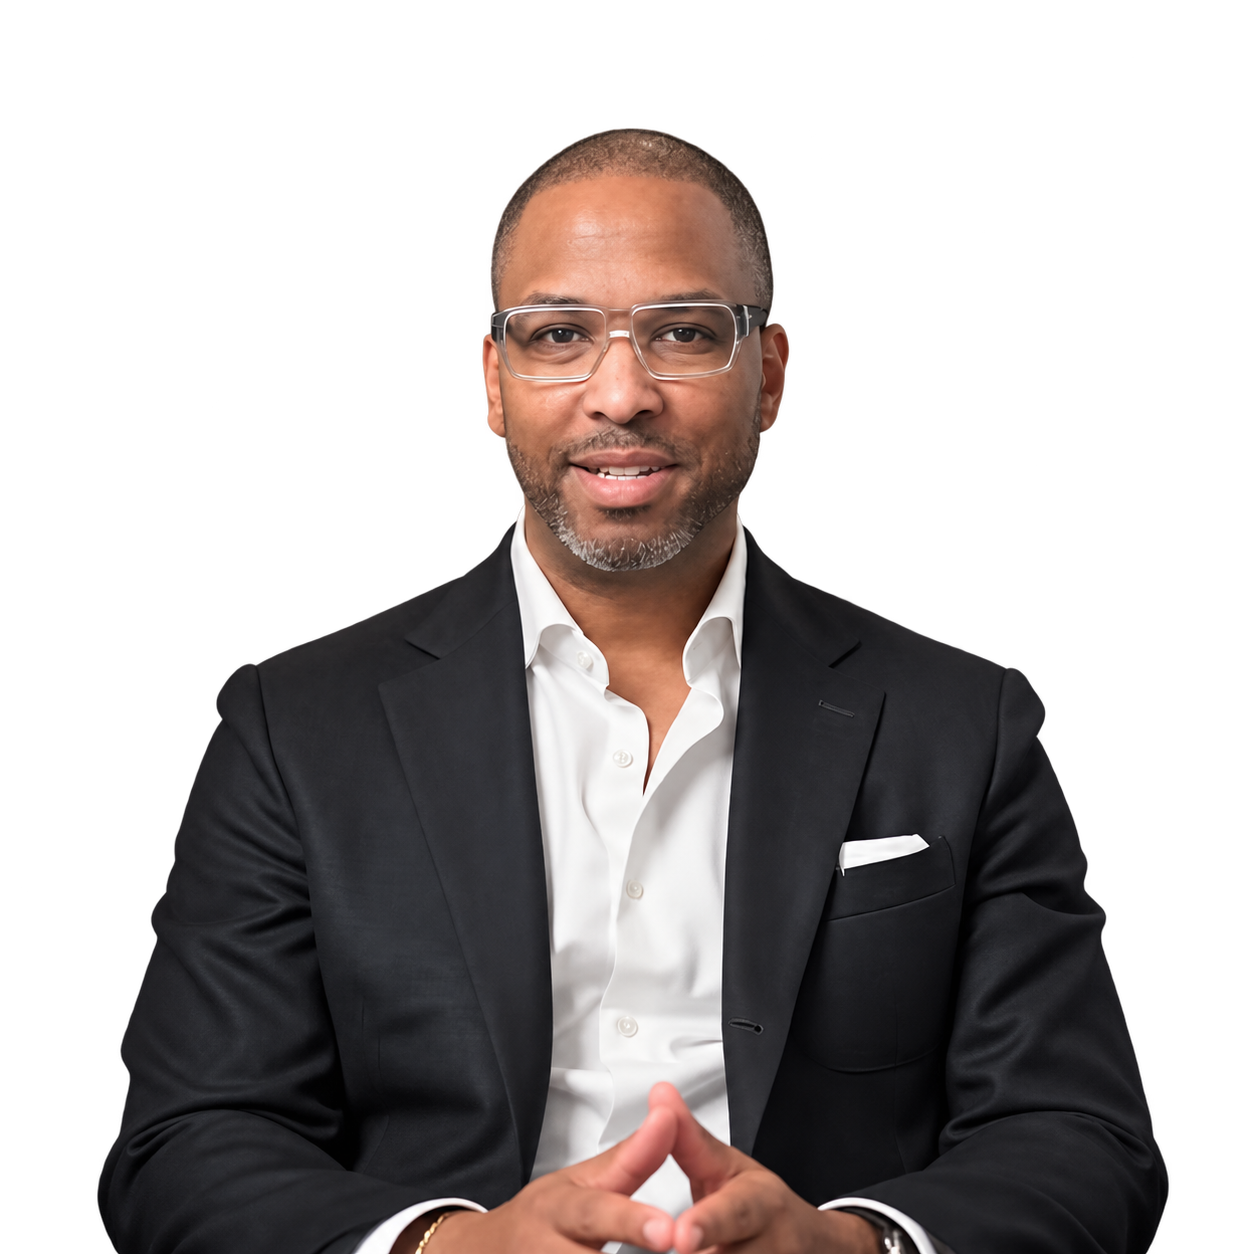
I'm Spencer Brawner, a Toronto-based security practitioner with an MBA, CISSP, CISM, and more than 20 years of experience building security programs. I write about AI security, privacy, and governance for organizations adopting AI tools and agents.
My current work examines what an agent is allowed to do, what a person actually approves, when an action can still be stopped, and what evidence explains the result. AISecurityGuy.blog brings together practical investigations and analysis for security leaders, founders, and practitioners making decisions about AI adoption.
What does AISecurityGuy.blog cover?
This blog explores how organizations can use AI while protecting sensitive information and maintaining control over consequential actions. I connect technical security questions with the governance decisions leaders need to make.
- AI agent security and approvals: permissions, approval scope, cancellation boundaries, and the evidence needed to investigate actions taken by agents.
- AI privacy and data protection: sensitive data exposure, informal AI use, data security posture management (DSPM), and privacy by design.
- AI governance and assurance: how frameworks such as ISO/IEC 42001 and SOC 2 inform controls, responsibilities, and evidence for AI systems.
- AI developer tooling: the security implications of the Model Context Protocol (MCP), agentic browsers, integrations, and access to local development environments.
- AI supply chains and Canadian considerations: dependencies on models, infrastructure, and providers, alongside privacy and governance questions relevant to Canadian organizations.
How I approach AI security
I start with the action, the information it touches, and the person or system responsible for the outcome. An approval button is useful only if it's clear what permission it grants. A cancellation control needs to explain whether it can still prevent execution. An audit record needs enough context to establish what happened.
I use practical investigations to examine those questions, then explain what the evidence supports and where it stops. When I describe a lab test, I distinguish the tested implementation from broader recommendations. Scripted-agent results don't establish how an autonomous model or a person will behave.
My professional perspective combines security program experience with business judgment. I look for controls that address a defined risk, fit the workflow, and produce evidence that technical teams and executive leaders can use.
Who is this blog for?
AISecurityGuy.blog is for security leaders evaluating AI adoption, founders building AI-enabled products, and practitioners implementing or supervising agents. Articles aim to help readers ask better vendor questions, identify gaps in a workflow, and decide what to test before relying on a control.
Some articles focus on Canadian privacy and governance considerations. Others examine technical questions that apply across jurisdictions. Framework and compliance discussions are educational; an organization's obligations depend on its activities, location, contracts, and the information it handles.
Start with these articles
- The API call hasn't run. Can you still cancel? explores why withdrawing approval can become ineffective before an external action executes.
- Integrating DSPM with ISO 42001 and AI Governance Frameworks connects data visibility with AI governance work.
- DSPM vs Traditional Data Security: Why AI Changes Everything examines data protection questions raised by AI adoption.
- ISO 42001 Implementation Guide for Canadian Organizations introduces the AI management system standard and implementation considerations.
- Privacy by Design for AI Systems explores privacy principles in AI system design.
You can also browse the latest articles.
Connect with Spencer Brawner
I'm based in Toronto, Ontario. To discuss an article, share a practical AI security question, or explore collaboration, connect with me on LinkedIn.